Skip to content
Archive

ZachXBT

40 posts collected

ZachXBT

@zachxbt

Scam survivor turned 2D investigator, Advisor @paradigm

1,986 Following 1.1M Followers 23.7K posts on X

This archive holds 40 posts and 14,656 replies back to 18 Nov 2025

Z zachxbt

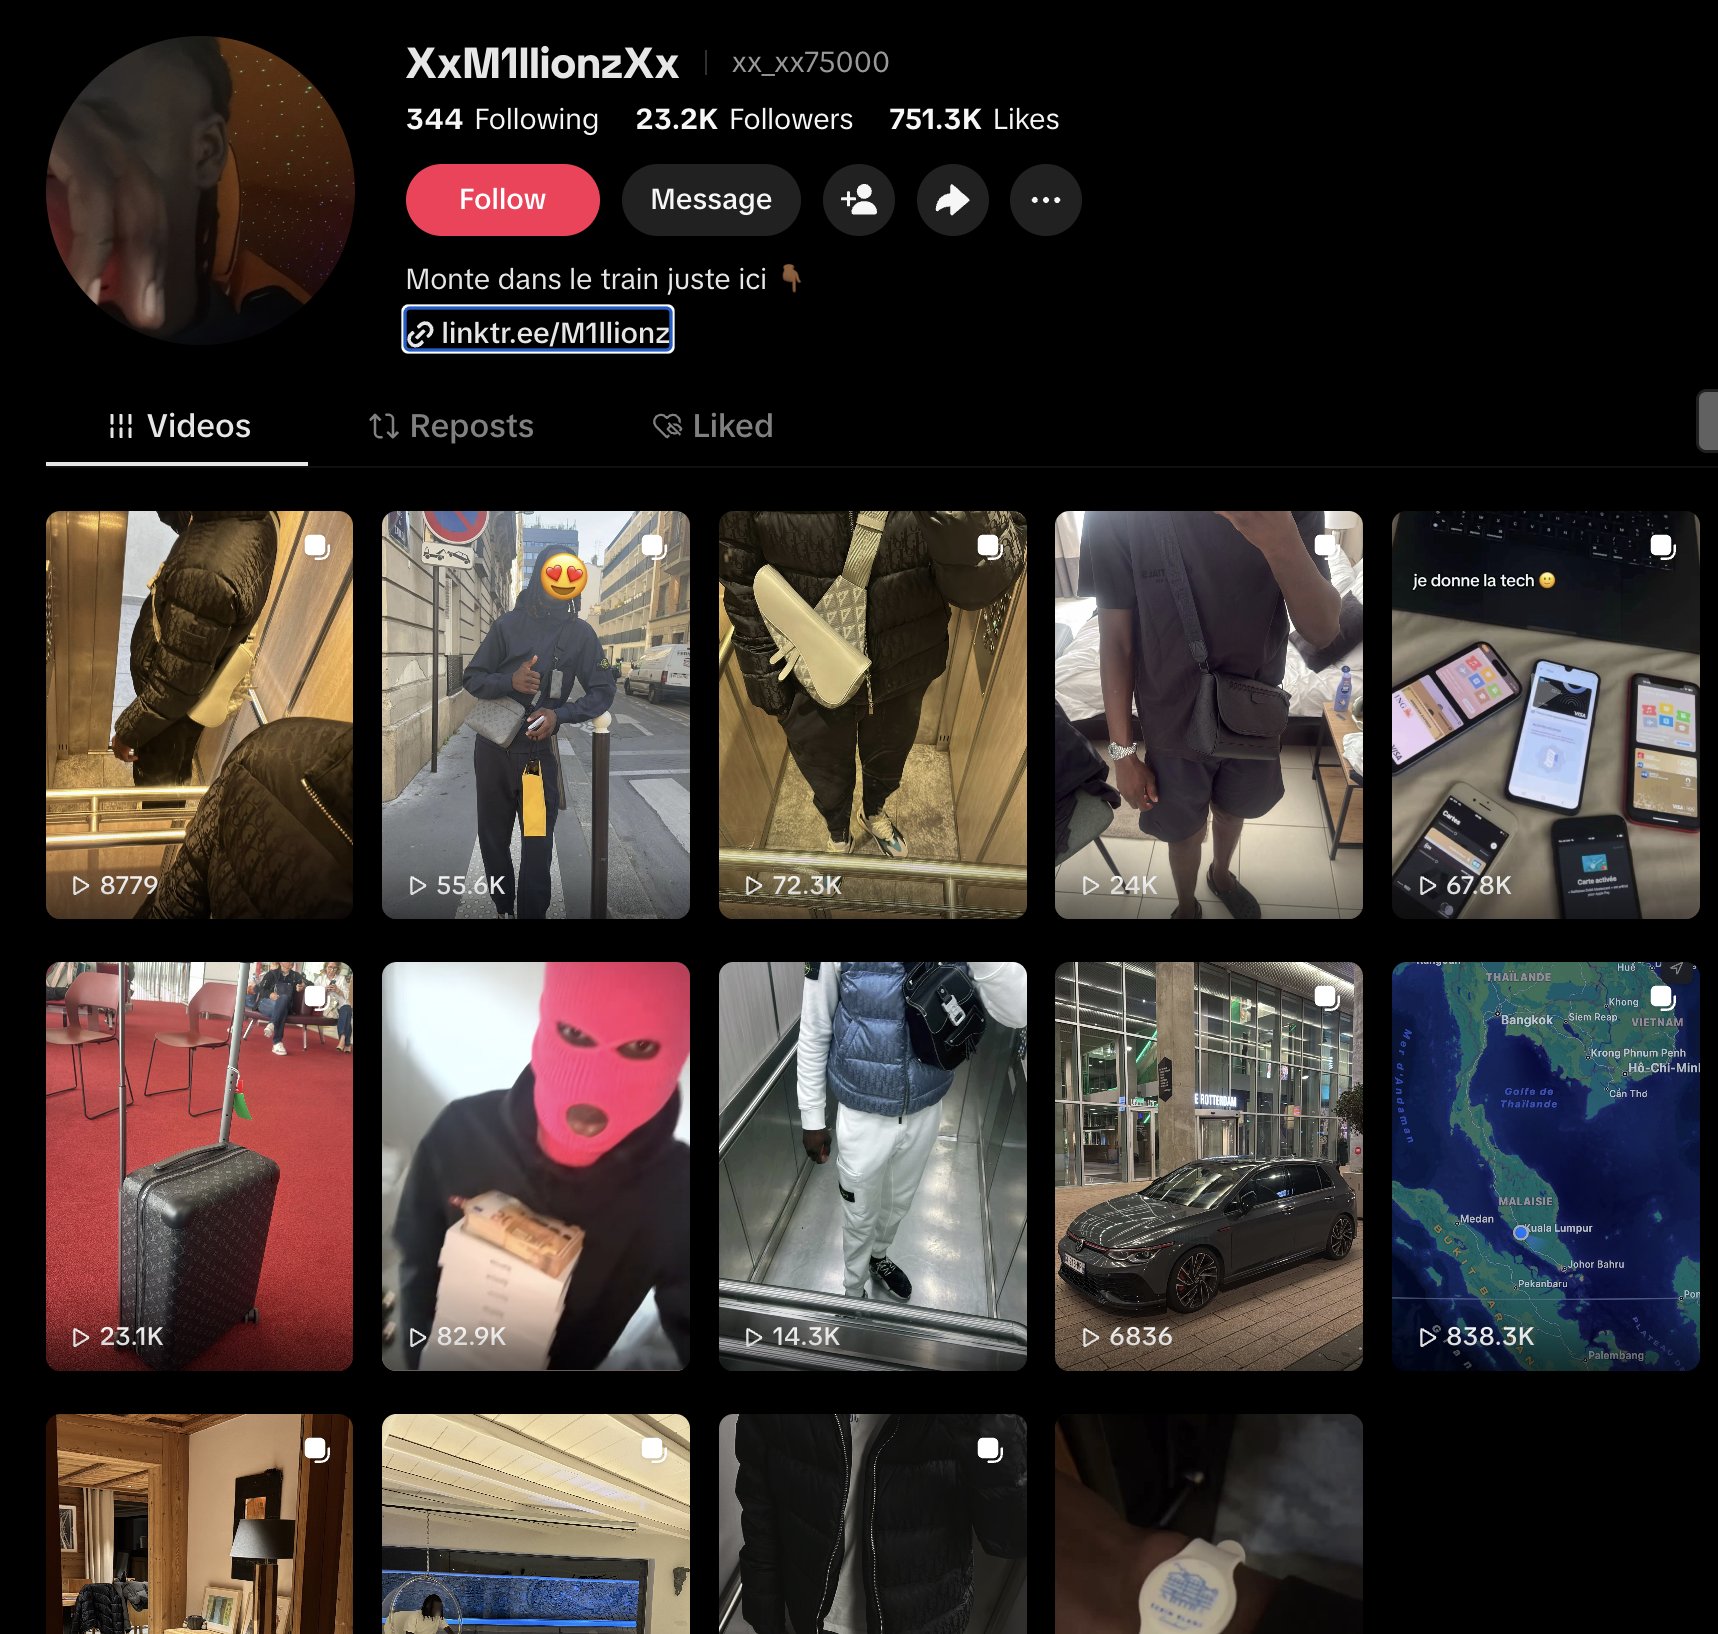
1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media. My work has led to a $93K t.co/0jIhg89aEW
650
Z zachxbt

Note they don’t deny having a data breach. Because they totally had a data breach.

1 9.1K
Z zachxbt

1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media. My work has led to a $93K t.co/0jIhg89aEW
624
Z zachxbt

1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media. My work has led to a $93K t.co/0jIhg89aEW
594
Z zachxbt

1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media. My work has led to a $93K t.co/0jIhg89aEW
570 1
Z zachxbt

1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media. My work has led to a $93K t.co/0jIhg89aEW
294
Z zachxbt

1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media. My work has led to a $93K t.co/0jIhg89aEW
218
Z zachxbt

1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media. My work has led to a $93K t.co/0jIhg89aEW
113
Z zachxbt

1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media. My work has led to a $93K Tether freeze directly tied to these attacks so far.

photo
553 763 8.3K 1.3M 2K
Z zachxbt

@BeardStaffX @littlewhaleB @BitMartExchange Why do so many victims lack basic common sense? You really expect me to have access to Bitmart internal system to reconcile all deposit, withdrawals, trades, etc or go raid its founder Sheldon Xia’s home? Go look in the mirror you kept your funds on a sketchy offshore bucked

2
Z zachxbt

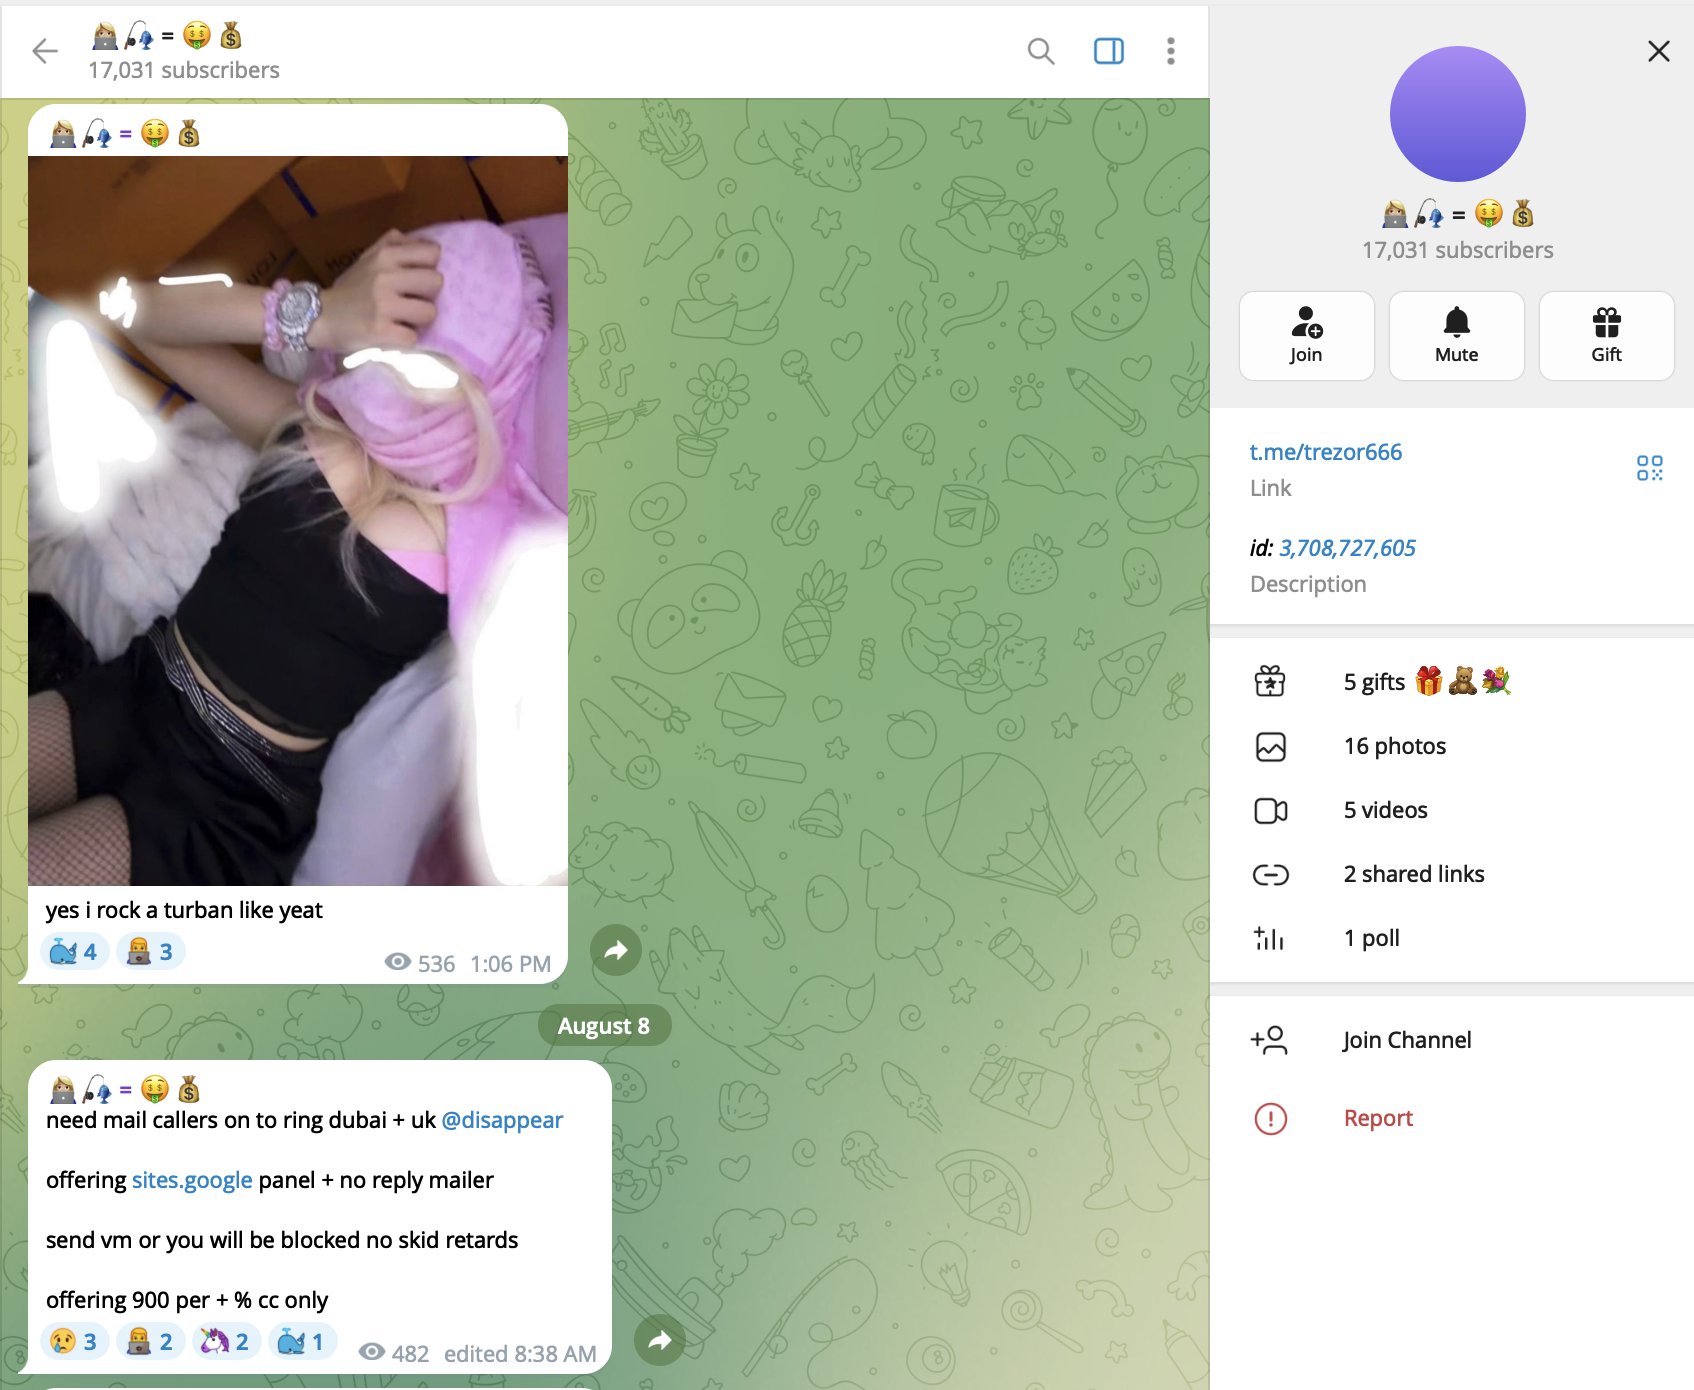
1/ Meet Tiffany Milanovich, a US based threat actor tied to at least $5M in thefts from hardware wallet and centralized exchange support impersonation scams. She's recorded herself taunting victims on calls after draining their funds. Tiffany openly flaunts luxury purchases, stolen funds, and casino gambling on social media.

photo
1K 961 10K 2.8M 3.3K

746 of 1,013 replies collected

Z zachxbt

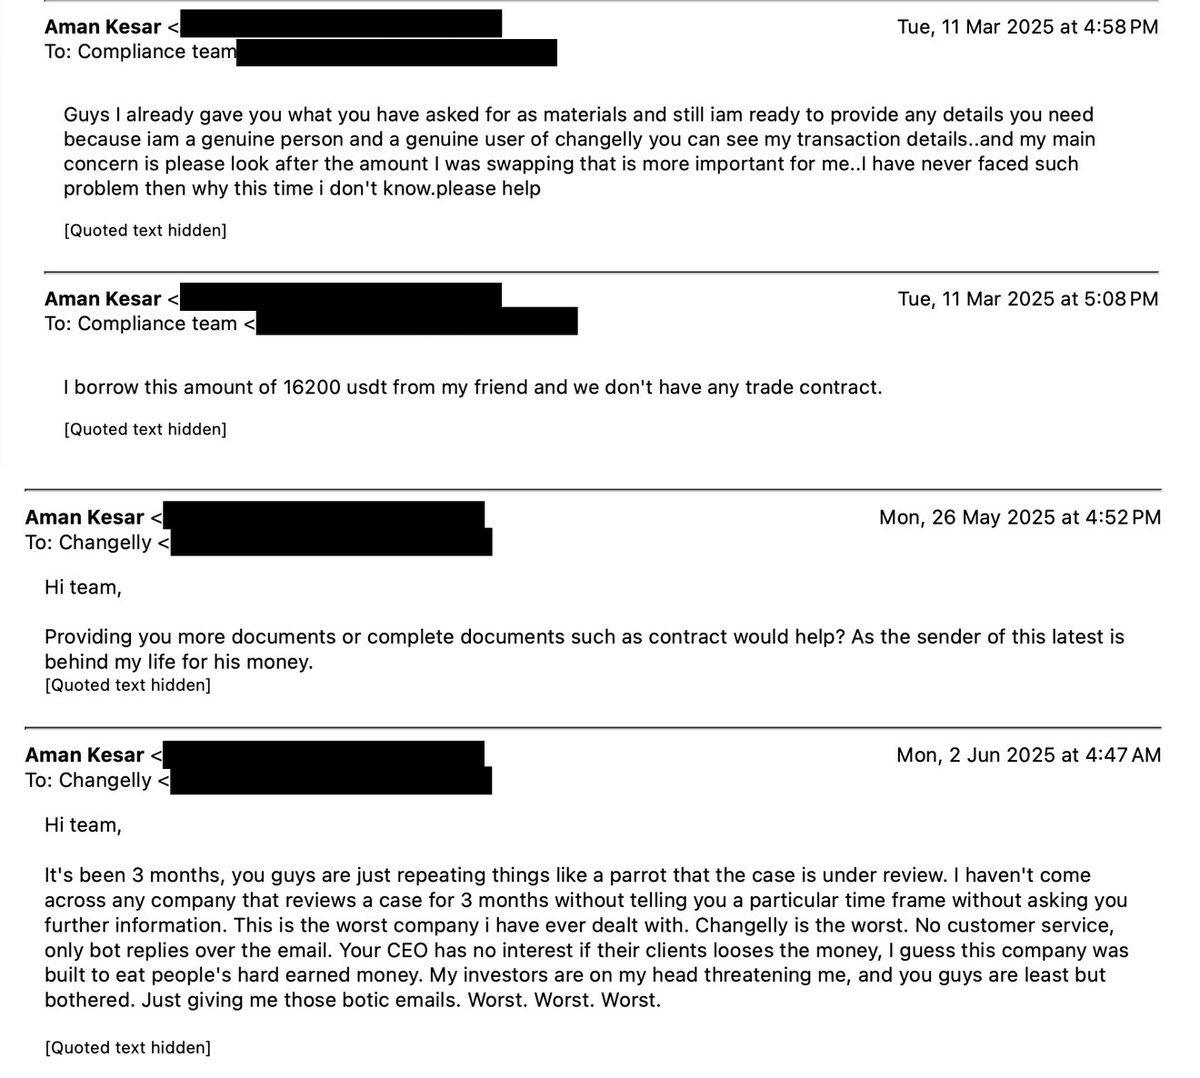
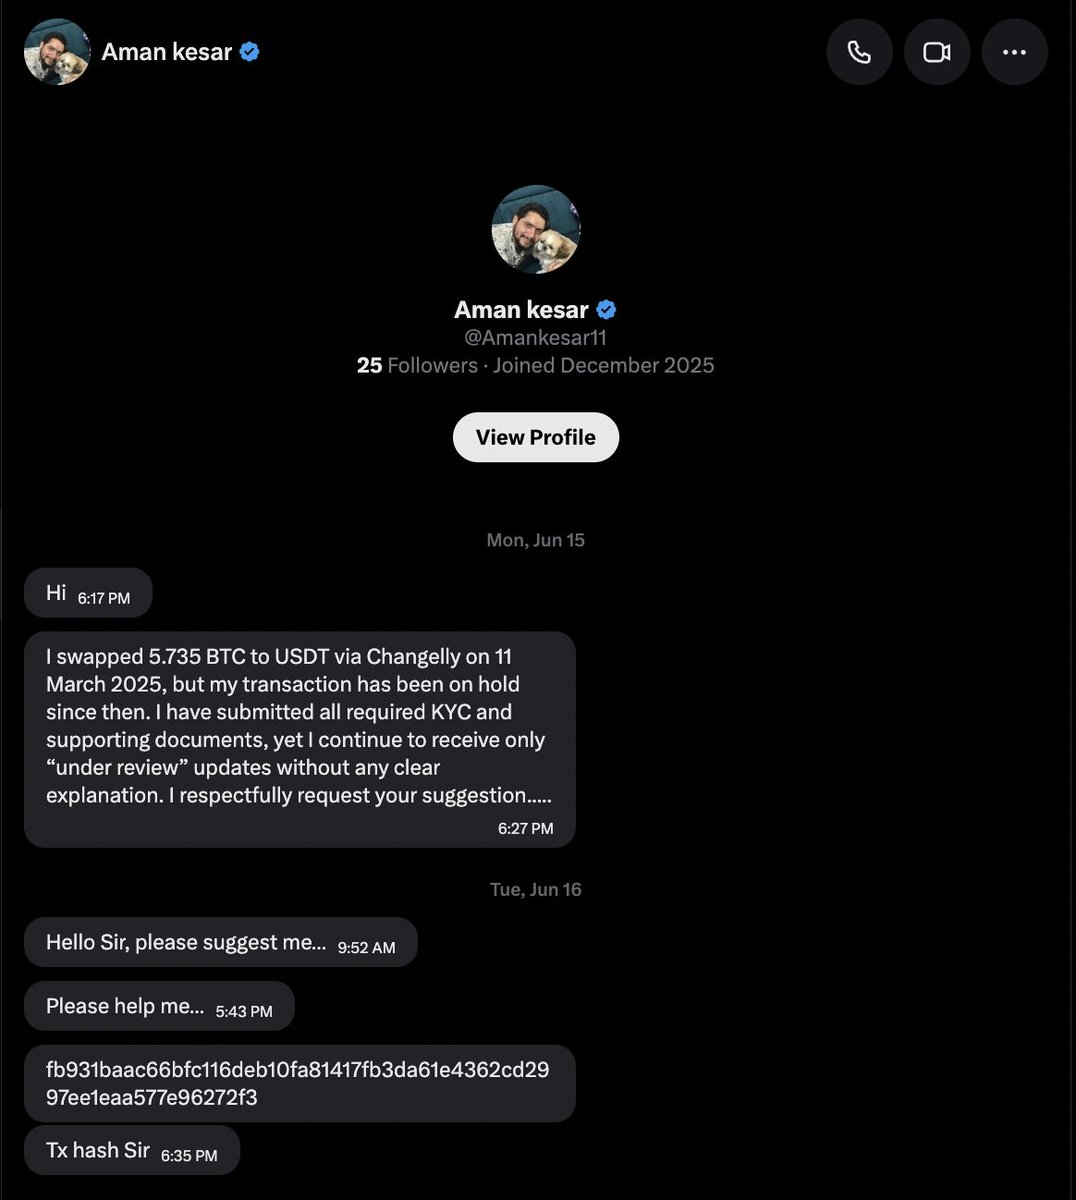
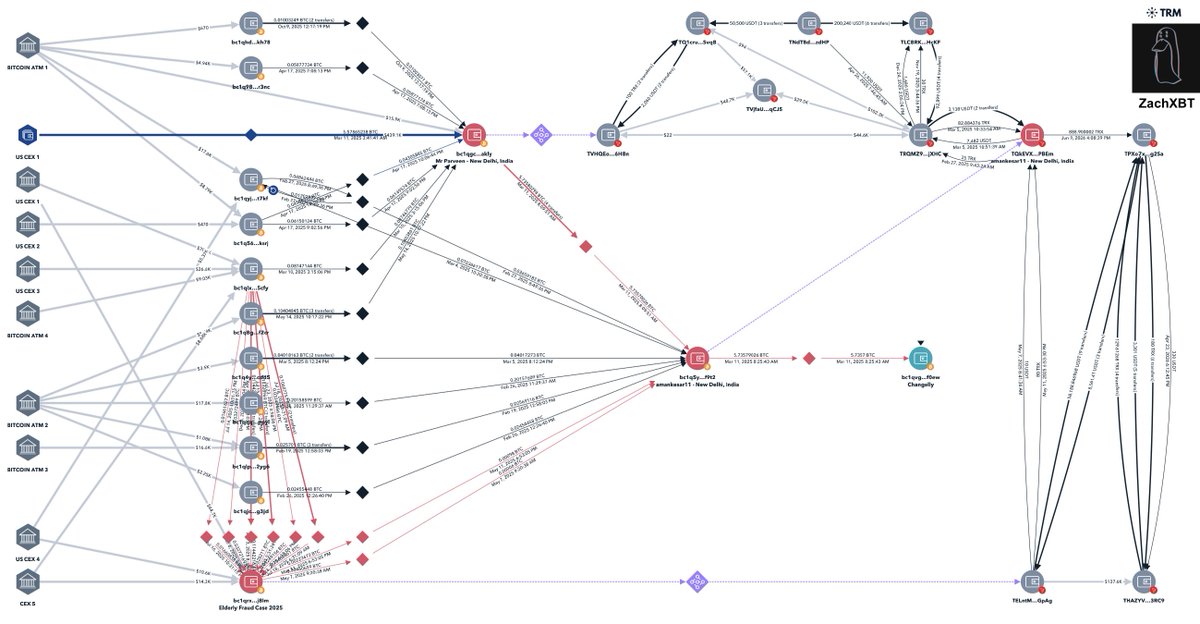
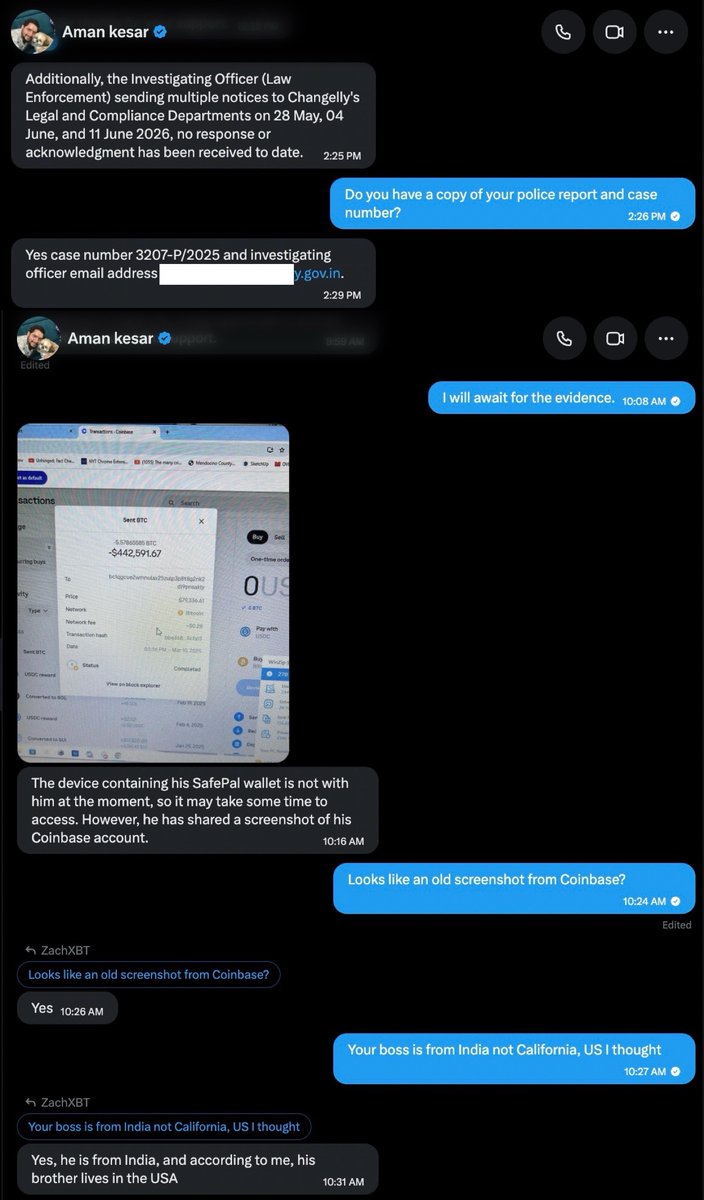
A short story about Indian scammers who called the cops on themselves: Earlier this week a follower DM'd me from his personal account complaining that 5.73 BTC ($475K) of his was 'unjustly' frozen at Changelly in Mar 2025. So I went and plotted the Bitcoin transaction in my compliance tools. The inflows trace back to illicit sources via social engineering thefts targeting Americans through US exchanges and Bitcoin ATMs. The broader cluster of high confidence thefts has taken $1M+ from victims since 2025, with several of them elderly. His story kept changing. It was a loan. No, his boss sent it. No, his boss invested in Bitcoin "during 2014 and 2015" through a friend in the US. The best part? In Dec 2025 he claims to have filed a police report in India over these frozen funds (3207-P/2025). In our DMs he shared email screenshots which I queried to surface more data points and map his group out. I suspect AmanKesar11 is a mule for his boss 'Mr Parveen,' as the 'proof' he sent included bank statements under a different name / location. While you can message me for help and I'll respect your privacy, at least use common sense and don't contact me with stolen funds. 5.73 BTC frozen order: fb931baac66bfc116deb10fa81417fb3da61e4362cd2997ee1eaa577e96272f3 AmanKesar11 BTC address: bc1q5yjxzcvfswvyx9y6cvlc3xe4laqqnqsjp3f9t2 AmanKesar11 Tron address: TQkEVXjtvSbigGa5fqFUpcYJnGvpKPPBEm

photo photo photo photo
545 368 3.8K 681K 677

428 of 545 replies collected

Z zachxbt

1/ An investigation into the opaque private loans/OTC, unilateral vesting changes, market maker coordination, unknown float, and >95% supply control behind $LAB's recent pump to $6B FDV. Here's why @LABtrade_ represents everything wrong with the current meta of retail extraction on major centralized exchanges.

photo photo
683 608 4.1K 1.3M 717

480 of 683 replies collected

Z zachxbt

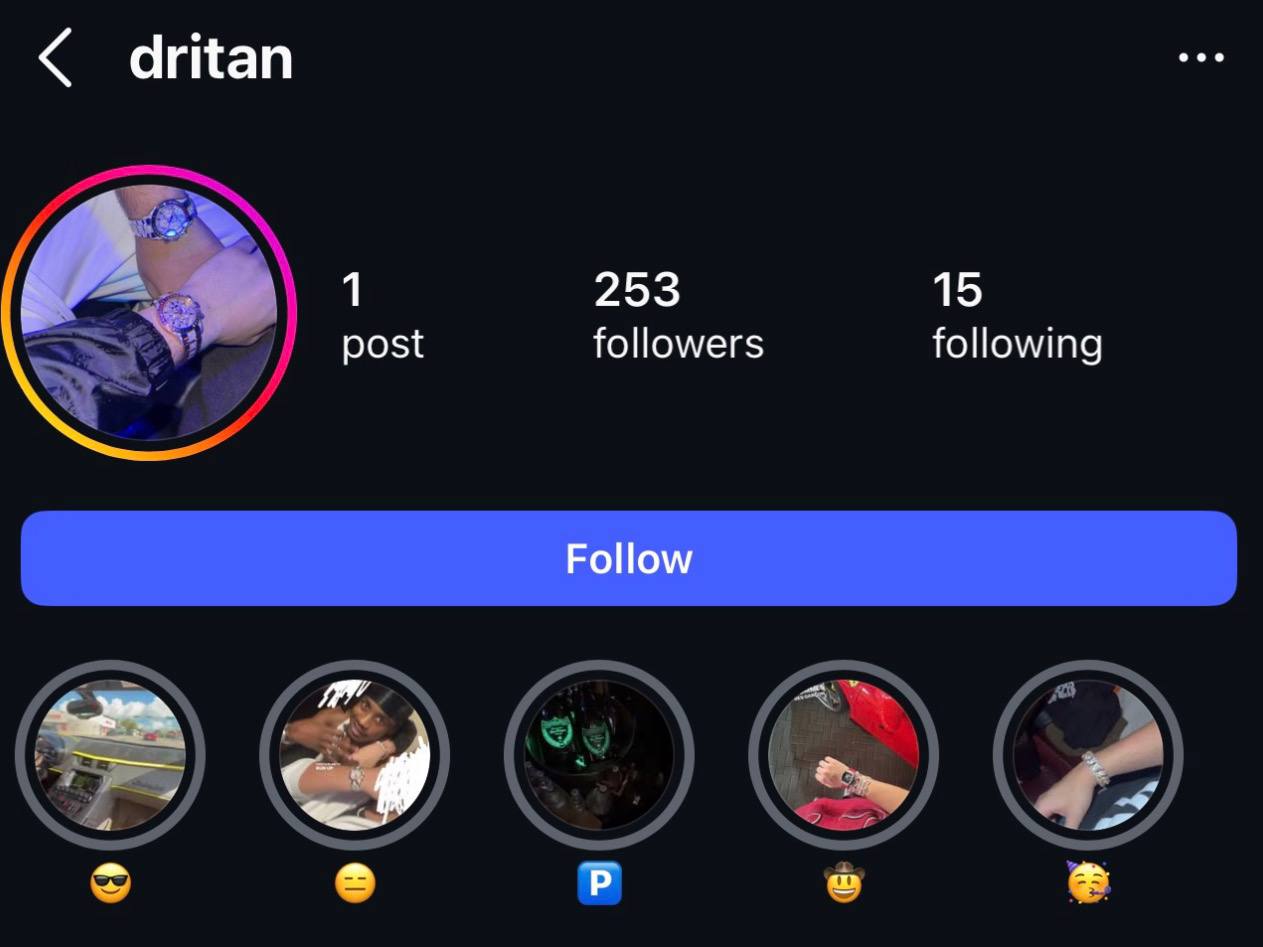
1/ Meet Dritan Kapllani Jr, a US based threat actor tied to $19M from social engineering thefts targeting crypto holders. Dritan flexes luxury cars, watches, private jets, & clubs all over social media. Recently he was recorded on a call showing off a wallet with stolen funds. x.com/zachxbt/status/205417000…

photo
812 685 7.3K 1.6M 2K

566 of 812 replies collected

Z zachxbt
ZachXBT @zachxbt ·

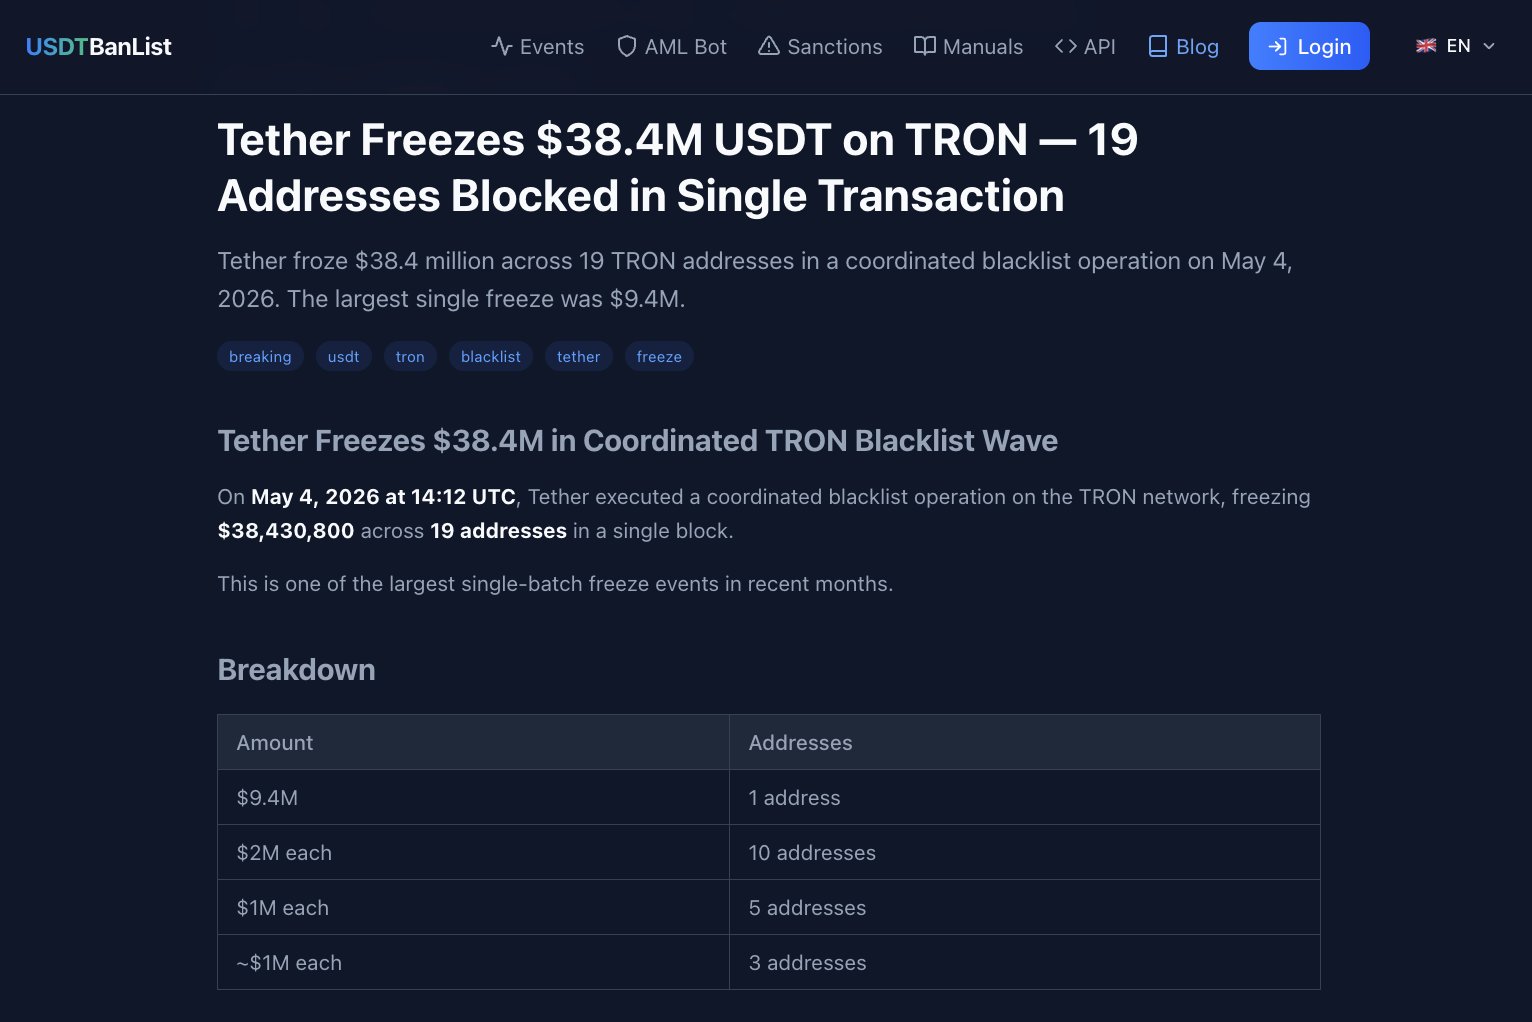
1/ The $150M+ DSJ Exchange (DSJEX) / BG Wealth Sharing Ponzi scheme collapsed last week. From April 27 – May 3, illicit actors laundered $92M+ across chains to obscure the trail. I helped lead an initiative with @Tether_to, @Binance Security Team, @OKX, & US law enforcement that has since frozen $41.5M+.

photo
322 280 2.1K 568K 314

273 of 322 replies collected

Z zachxbt

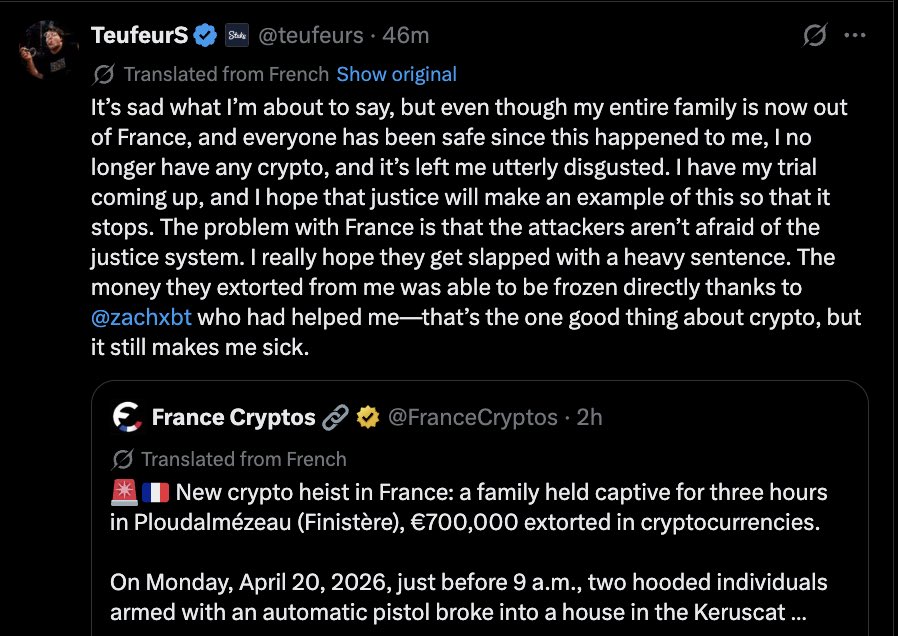
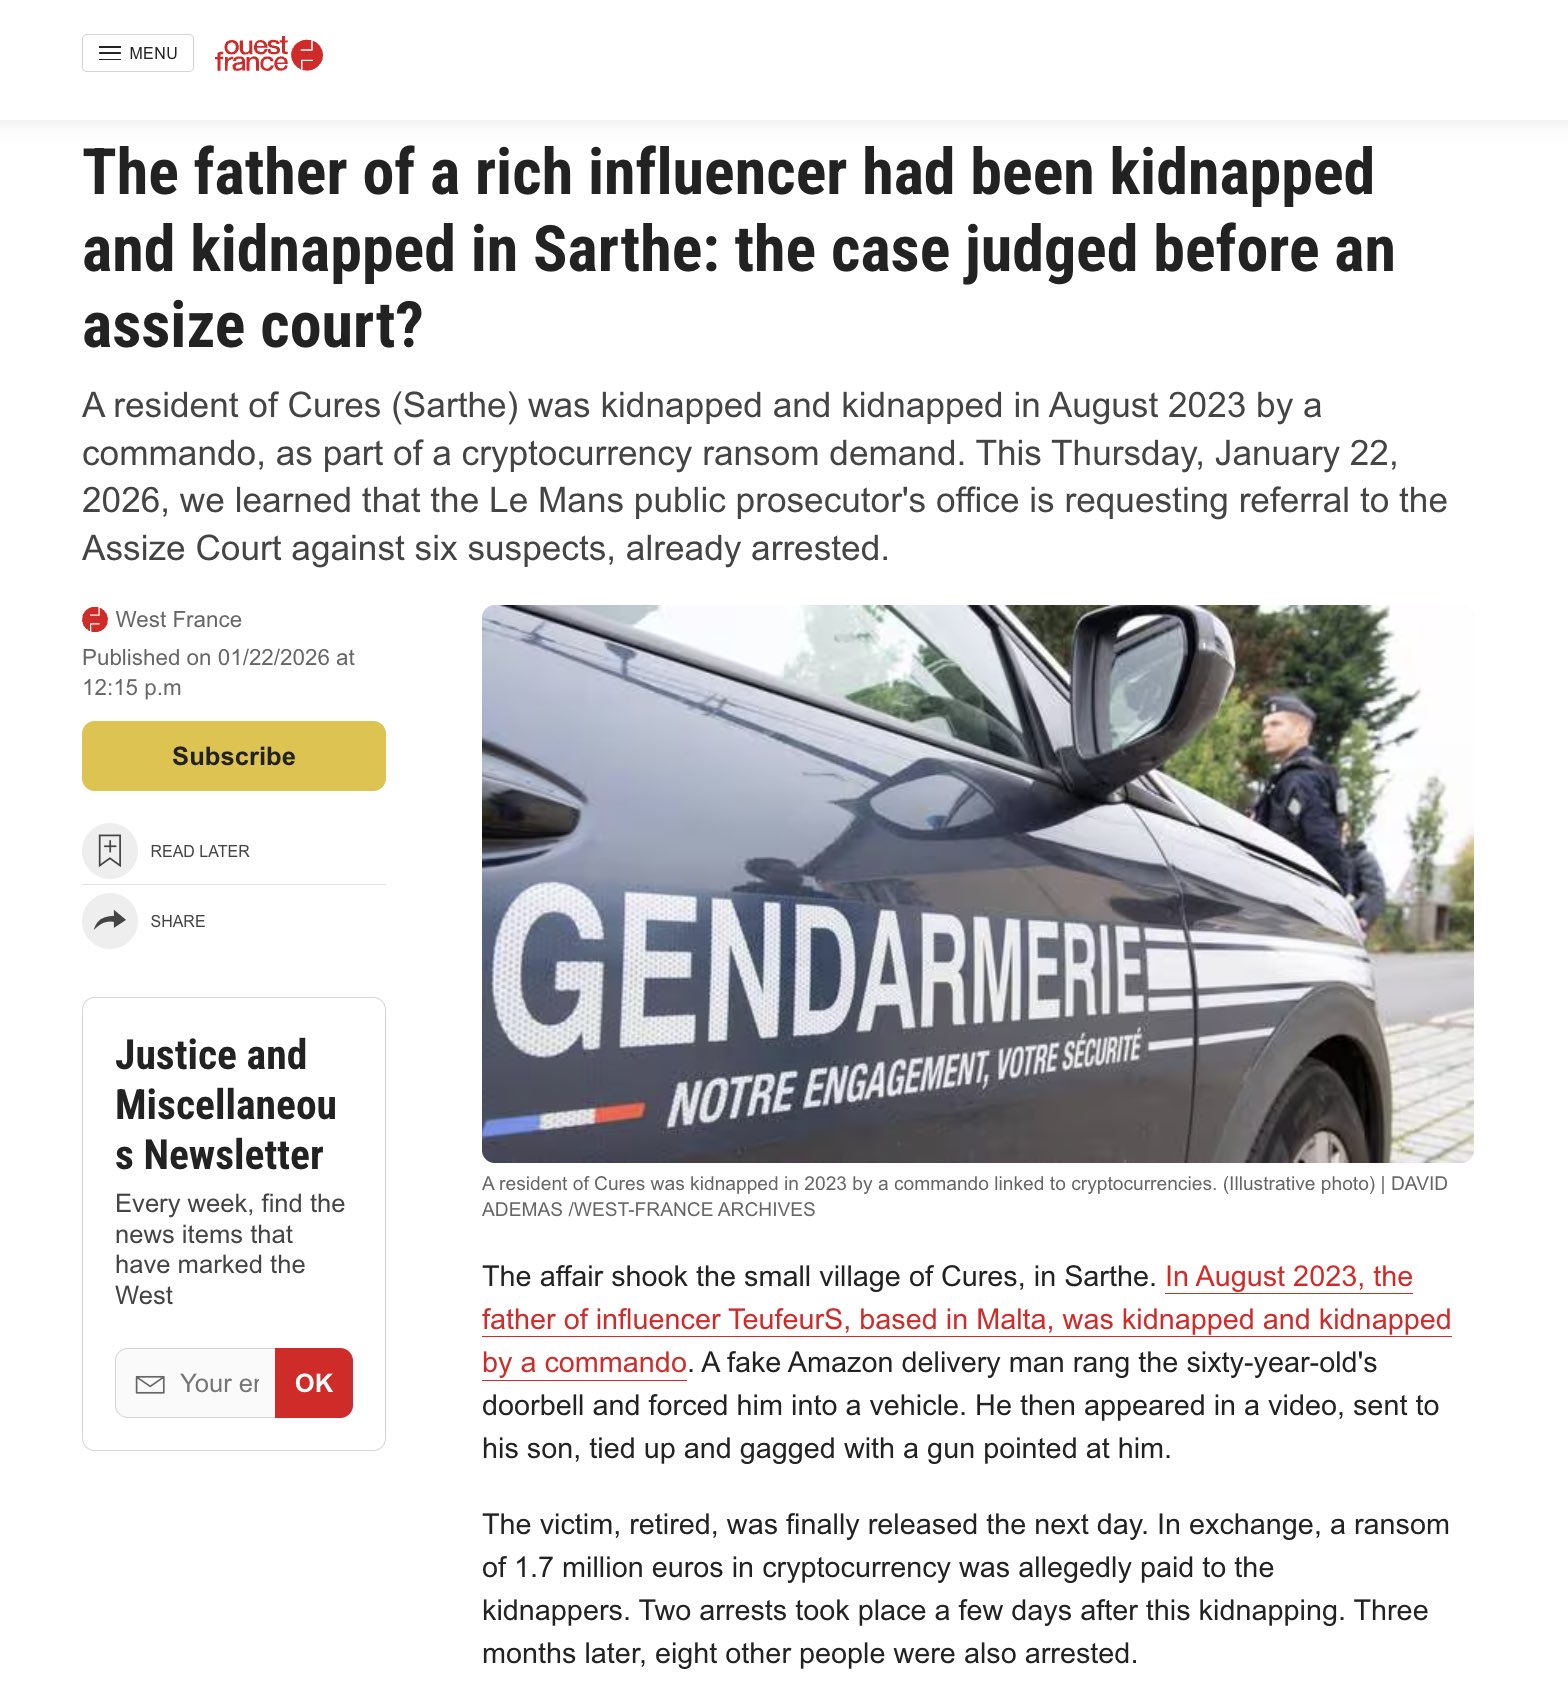
In late 2023, French streamer TeufeurS was extorted for a ransom after a family member was kidnapped in France. I can finally share that I helped lead efforts that resulted in an ~$800K freeze with the Binance Security team after a $2M ransom was paid. Six suspects tied to the incident were later arrested. Given the sensitivity of the case, I held off commenting until now. I have since assisted with asset freezes and identifying culprits in several of the recent France home invasion robberies, and hope to share details in the coming months. If you or someone you know falls victim, reach out as soon as possible rather than delay. I prioritize these types of cases as they have grown more frequent amidst this disturbing trend.

photo photo
682 666 7.3K 1.2M 622

532 of 682 replies collected

Z zachxbt

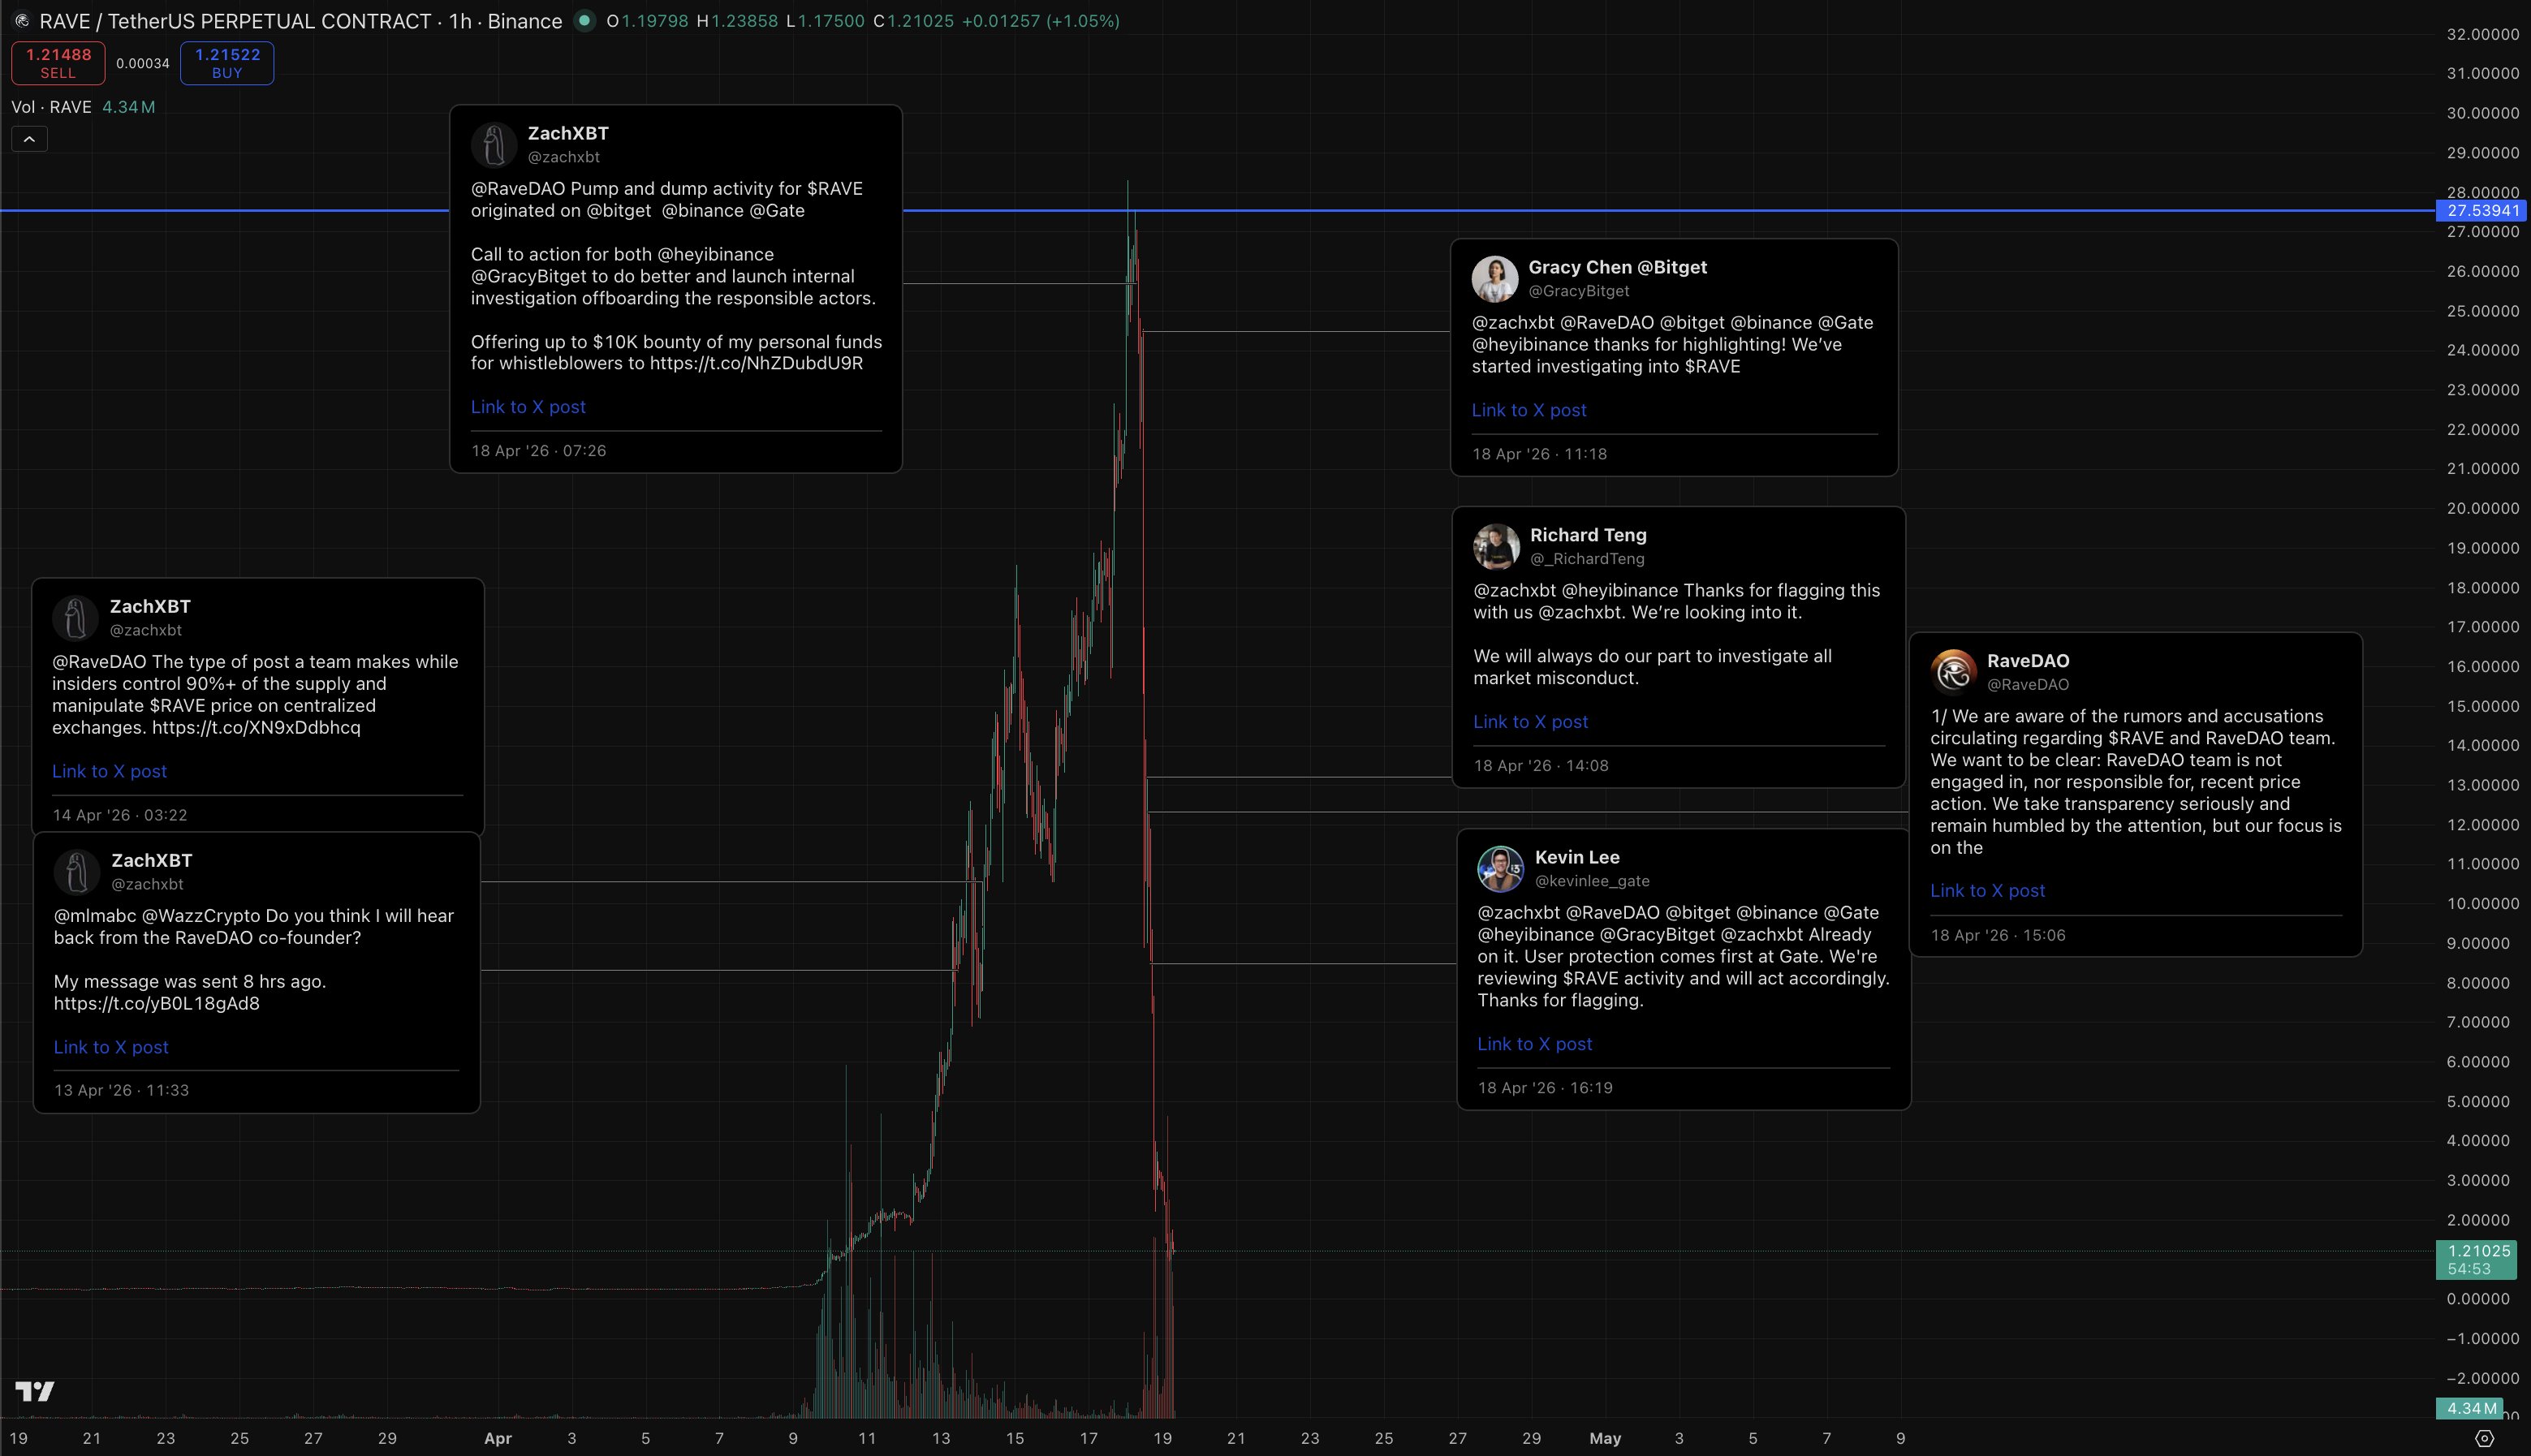
A summary of the RAVE -95% price fluctuation from $26 to $1 over the past 24 hours. RAVE Timeline: April 18, 2026 7:26 am UTC: I posted a call to action for Binance, Bitget, & Gate to investigate RAVE market manipulation and offered a $10K bounty. 10:56 am UTC: I posted an update increasing the bounty to $25K. 11:18 am UTC: Bitget publicly acknowledged the call to action. 2:08 pm UTC: Binance publicly acknowledged the call to action. 3:06 pm UTC: RaveDAO posted claiming they have no involvement. 4:19 pm UTC: Gate publicly acknowledged the call to action. In the days leading up, on April 13 & 14, I confronted RaveDAO co-founder Yemu Xu (wildwoomoo) but have yet to receive an answer. RAVE launched in Dec 2025 on Binance Alpha with a 1B total supply. The addresses below, linked to the initial distribution, control ~95% of the RAVE supply (h/t Mlm): 0x9831156F1a6E506Fca41503590b42F07c2e80f54 0x8Ed6245C3276307E1A9D9Dc872E98A0E770070fd 0x6020656d1EF182173E45D4Fc375BDD5a48c674B0 0x2664cB80a5ee7D8EC05fe7C752dD62E078056E6d 0x2D81F8AeBf3e58A5e638006c9fd8F38C5220ecab 0x31694d761A8e851cFFbCd286aC54D01e5Ce5aFe6 0x0A1F07993a51CcEb4f52CA67765AECeADDA790d7 0xEB74Df8588cFC1C179Df4bd96C0bB8B227B9bE92 0x53d7d52301366DC14E1916b14eFeC1aDD8F3487b I found suspicious CEX activity in April 2026 tied to RaveDAO team addresses onchain, which potentially contradicts their recent statement: Bitget 0x2dc20f2180582172f5450c5d71e23fa438a7031b 0xa3a02aeb97fc1737c66f50d07d024799c137891d 0x2d95eb42525e6087e0cb7869f98da6838ed2e743 Gate 0x31711246b05d71e9eda5e38a3abb654020ee3353 Given the supply concentration, the team at minimum knows who is responsible for this price action. A simple litmus test: $6B in market cap was wiped out on just $52M of 24hr liquidations (h/t CoinGlass). That ratio points to a manipulated and unsustainable valuation. RAVE is not the only token with manipulation we have seen on major centralized exchanges. It's just the most blatant, reaching a top 15 market cap within 10 days before dropping 95% in hours. Other projects with highly questionable price action recently include: SIREN, MYX, COAI, M, PIPPIN, RIVER. Exchanges need faster intervention on manipulation. Detection at scale isn't easy, but each day of delay means retail traders absorb losses while platforms collect fees on the volume. The outcome is the same regardless of intent. While it's good the exchanges responded, I find it unlikely this activity wasn't spotted internally before I raised it publicly. I recognize how much this behavior takes from retail traders, and I plan to investigate similar movements in hopes of identifying the responsible parties. I want to reiterate that I did not take a position. If I had, I would have been liquidated myself. I also could not anticipate if or when the exchanges would comment publicly. My $25K bounty will remain active since the only DMs received were unverified claims rather than non-public information with supporting evidence as requested.

photo
1.2K 1.2K 7.1K 1.2M 954

577 of 1,154 replies collected

Z zachxbt
ZachXBT @zachxbt ·

1/ Recently an unnamed source shared data exfiltrated from an internal North Korean payment server containing 390 accounts, chat logs, crypto transactions. I spent long hours going through all of it, none of which has ever been publicly released. It revealed an intricate ~$1M/month scheme of fraudulent identities, forged legal documents, and crypto-to-fiat conversion. Enjoy the findings!

photo
333 866 6K 1.1M 2K

283 of 333 replies collected

Z zachxbt
ZachXBT @zachxbt ·

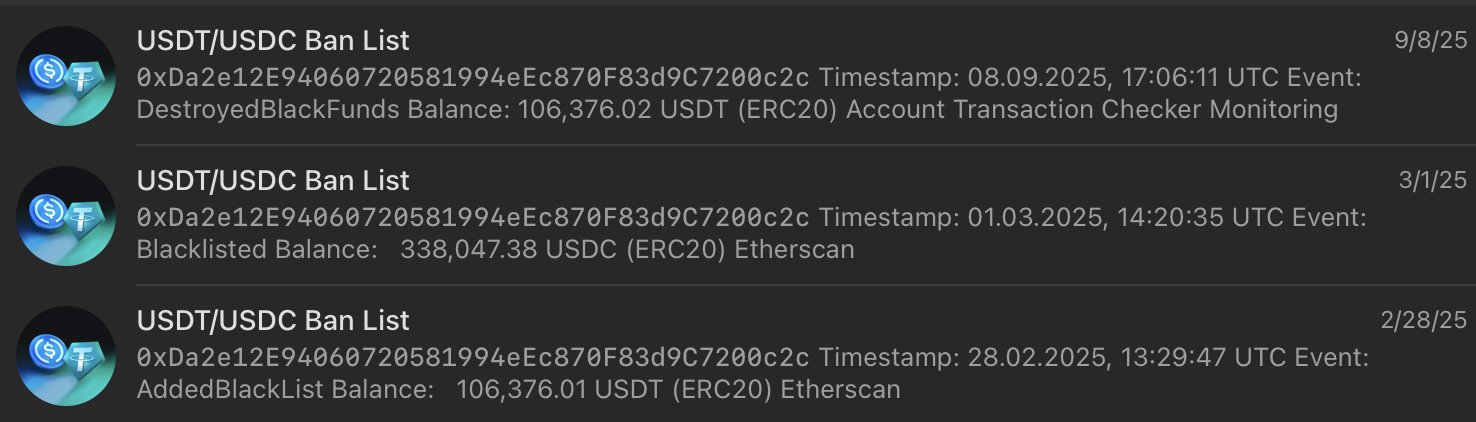
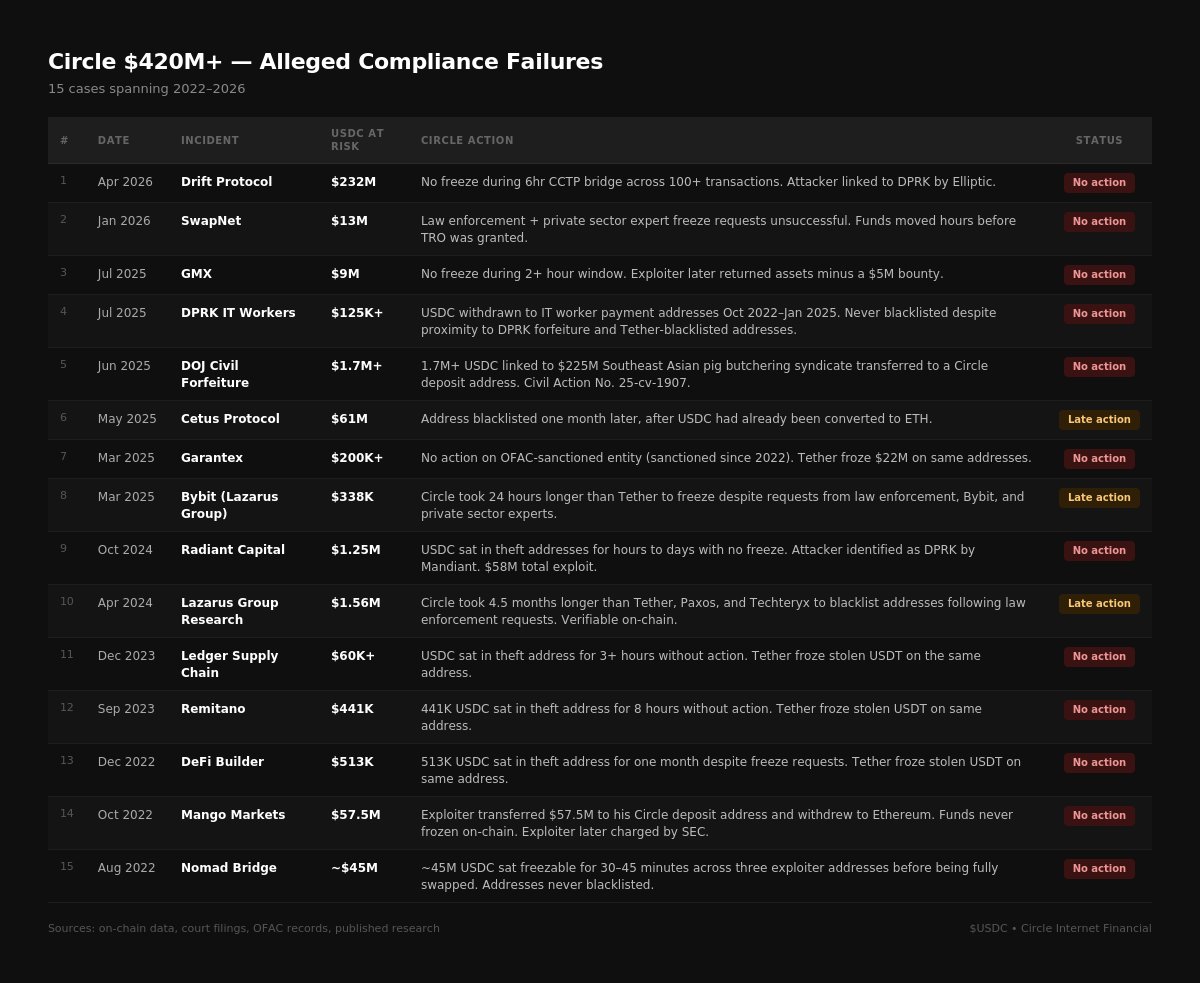
17/ On February 21, 2025, Bybit was hacked by Lazarus Group for $1.5B, widely reported across mainstream media. On February 28, 106K USDT and 338K USDC consolidated to theft address 0xDa2. Law enforcement, Bybit, and private sector experts submitted freeze requests to both Tether and Circle. Tether froze the address within hours. Circle took 24 hours longer to act. Theft address: 0xDa2e12E94060720581994eEc870F83d9C7200c2c

photo
@

How about you tell the entire community why Circle has yet to freeze 115K USDC directly tied to the Bybit hack by DPRK with zero obfuscation after 5 hours? Meanwhile Tether already froze 106K USDT multiple hours ago....

7 25 341 182K 21

5 of 7 replies collected

Z zachxbt
ZachXBT @zachxbt ·

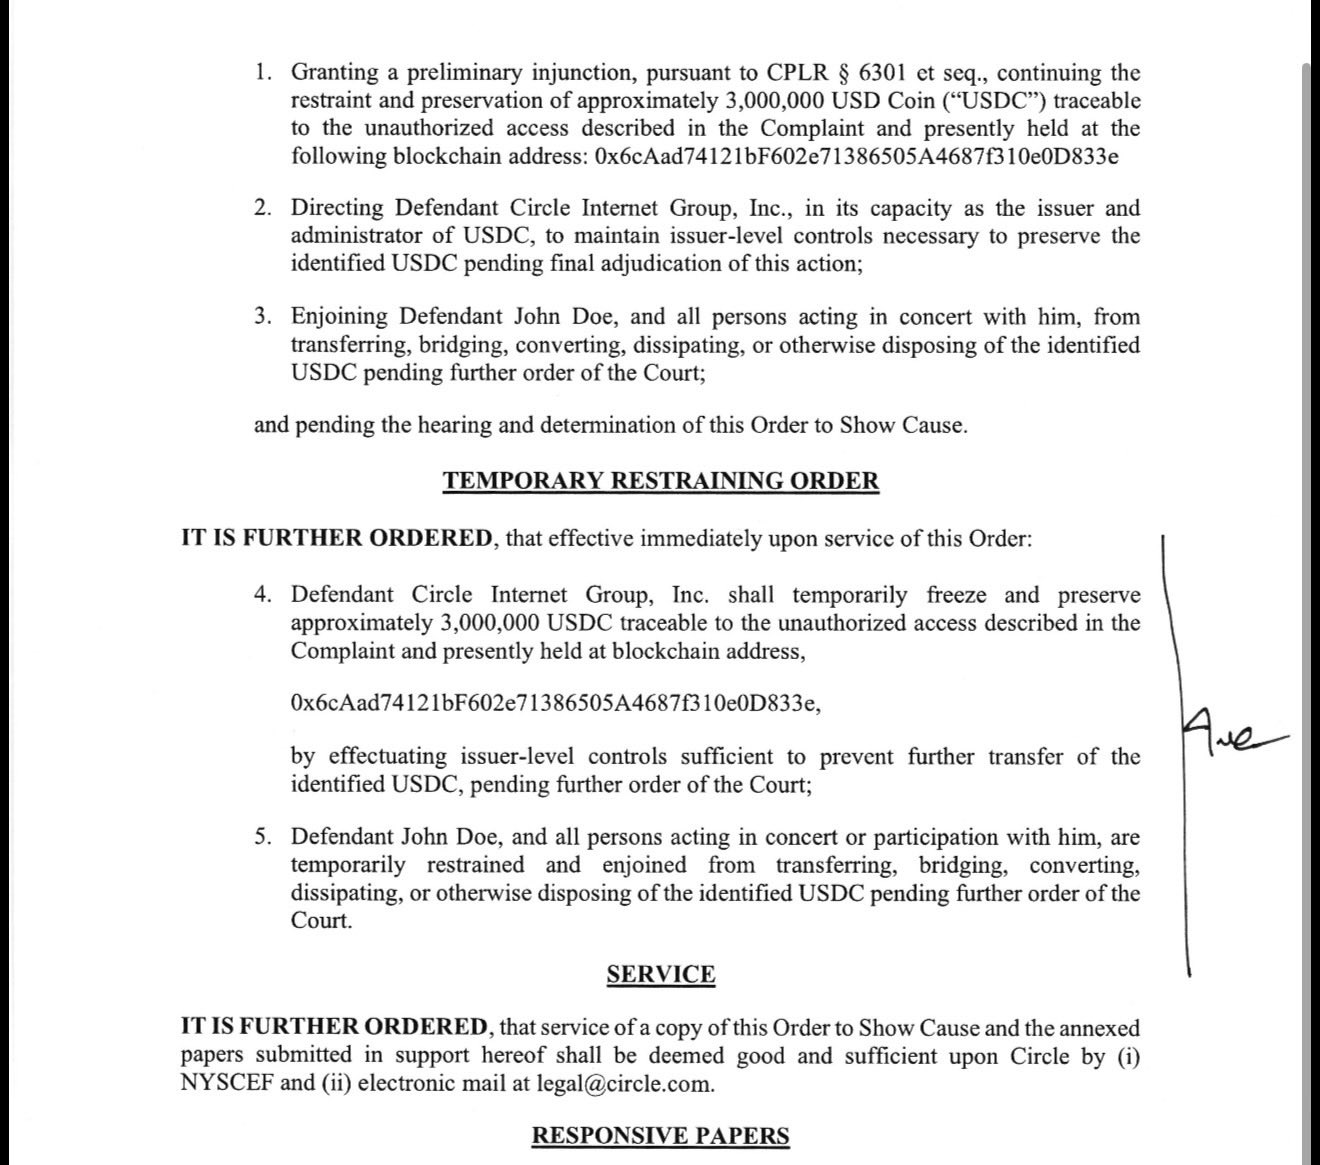
4/ On January 25, 2026, SwapNet was exploited for $16M. 3M USDC sat in the exploiter's address for two days. Both law enforcement and private sector experts submitted temporary freeze requests to Circle for the theft address. Both were unsuccessful. One victim pursued a New York court order. The funds were swapped hours before the TRO was granted. Theft address: 0x6cAad74121bF602e71386505A4687f310e0D833e

photo
@

History has shown that Circle is a bad actor. SwapNet contracts were exploited for $13M USDC on Base ~10 hours ago. 3M USDC is still sitting freezable at 0x6cAad74121bF602e71386505A4687f310e0D833e Why should anyone c...

3 6 372 98K 13

1 of 3 replies collected

Z zachxbt
ZachXBT @zachxbt ·

3/ On April 1, 2026, Drift Protocol was exploited for $280M. The exploiter used CCTP to bridge 232M+ USDC from Solana to Ethereum across 100+ transactions over six consecutive hours. 10+ additional DeFi protocols across the Solana ecosystem were indirectly impacted. Despite the attacker laundering funds over six consecutive hours across Circle's own native bridge, no USDC was frozen. The attacker has been linked to DPRK by Elliptic. Theft address: HkGz4KmoZ7Zmk7HN6ndJ31UJ1qZ2qgwQxgVqQwovpZES

@

Update: $230M+ USDC bridged via CCTP from Solana to Ethereum across 100+ txns. 6 hours is how long Circle had to freeze stolen funds from the $280M+ Drift hack. Circle is a centralized stablecoin issuer headquartered...

15 19 557 114K 24

9 of 15 replies collected

Z zachxbt

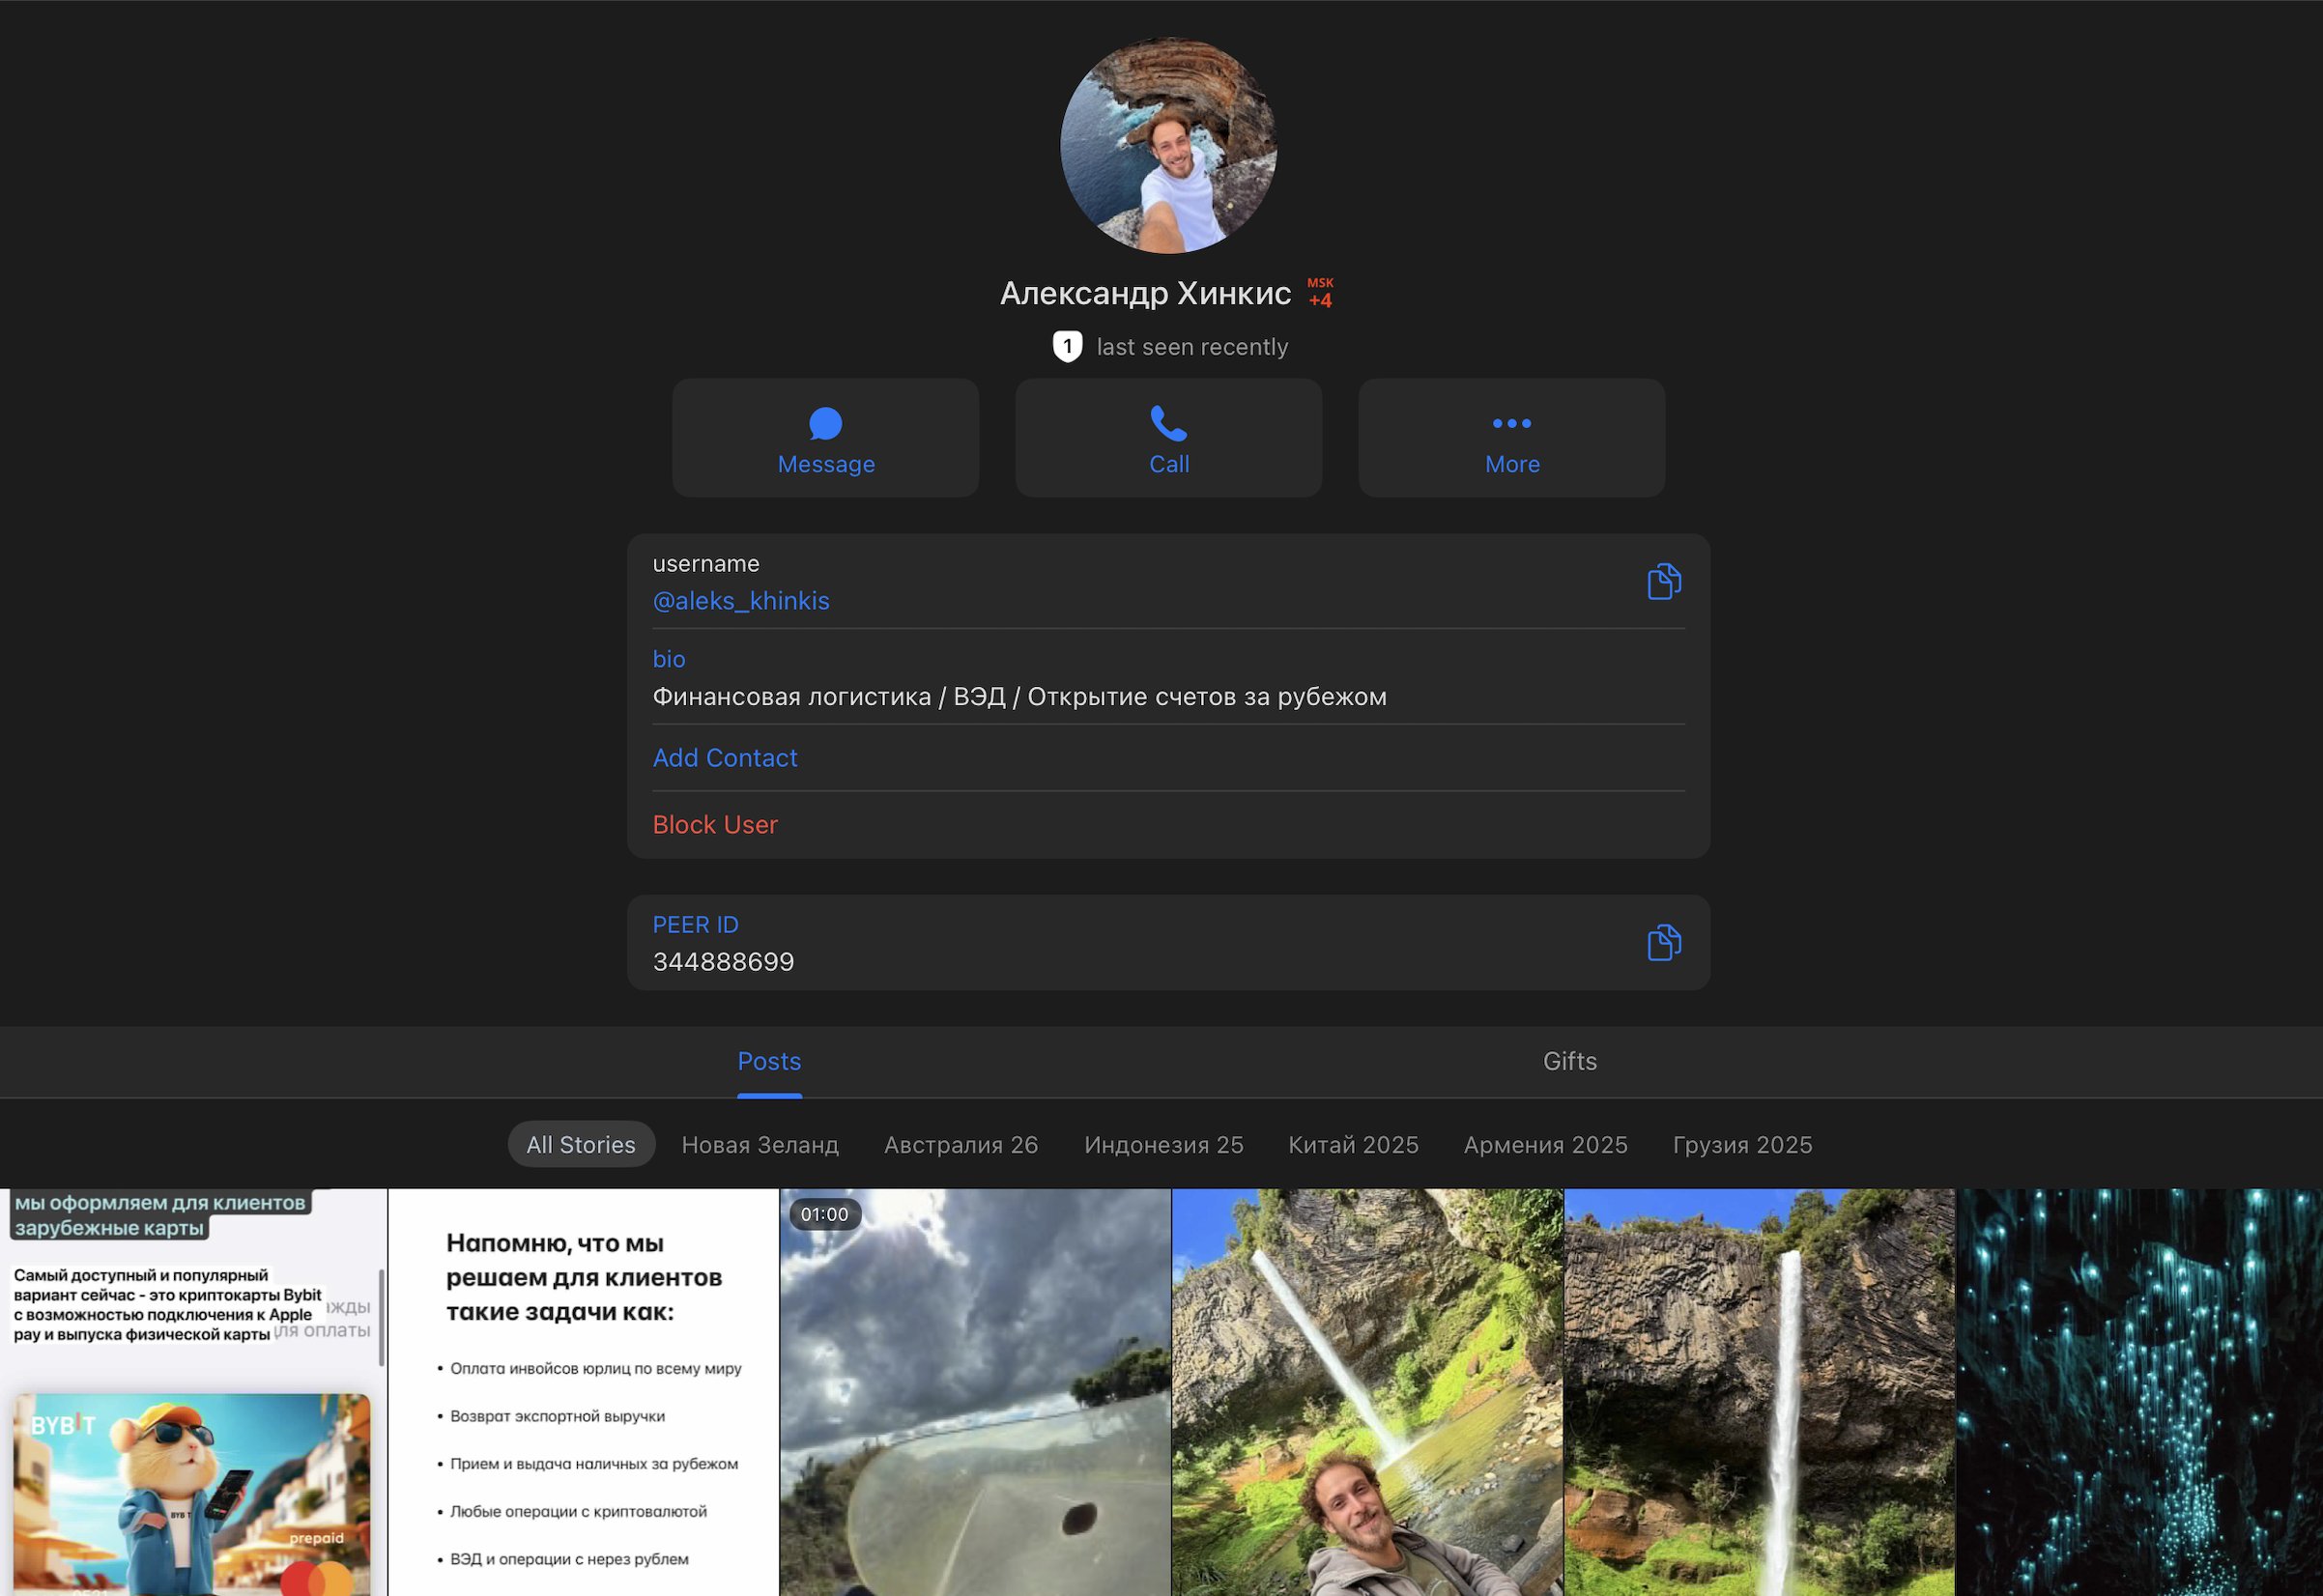
1/ Meet Aleksandr (Aleks) Khinkis, a Russian OTC broker who has allegedly helped a ransomware group launder $4.7M+ via a single crypto exchange account since July 2025, across three suspected ransom payments totaling 796 BTC. x.com/zachxbt/status/203643084…

photo
307 343 3.3K 456K 686

264 of 307 replies collected